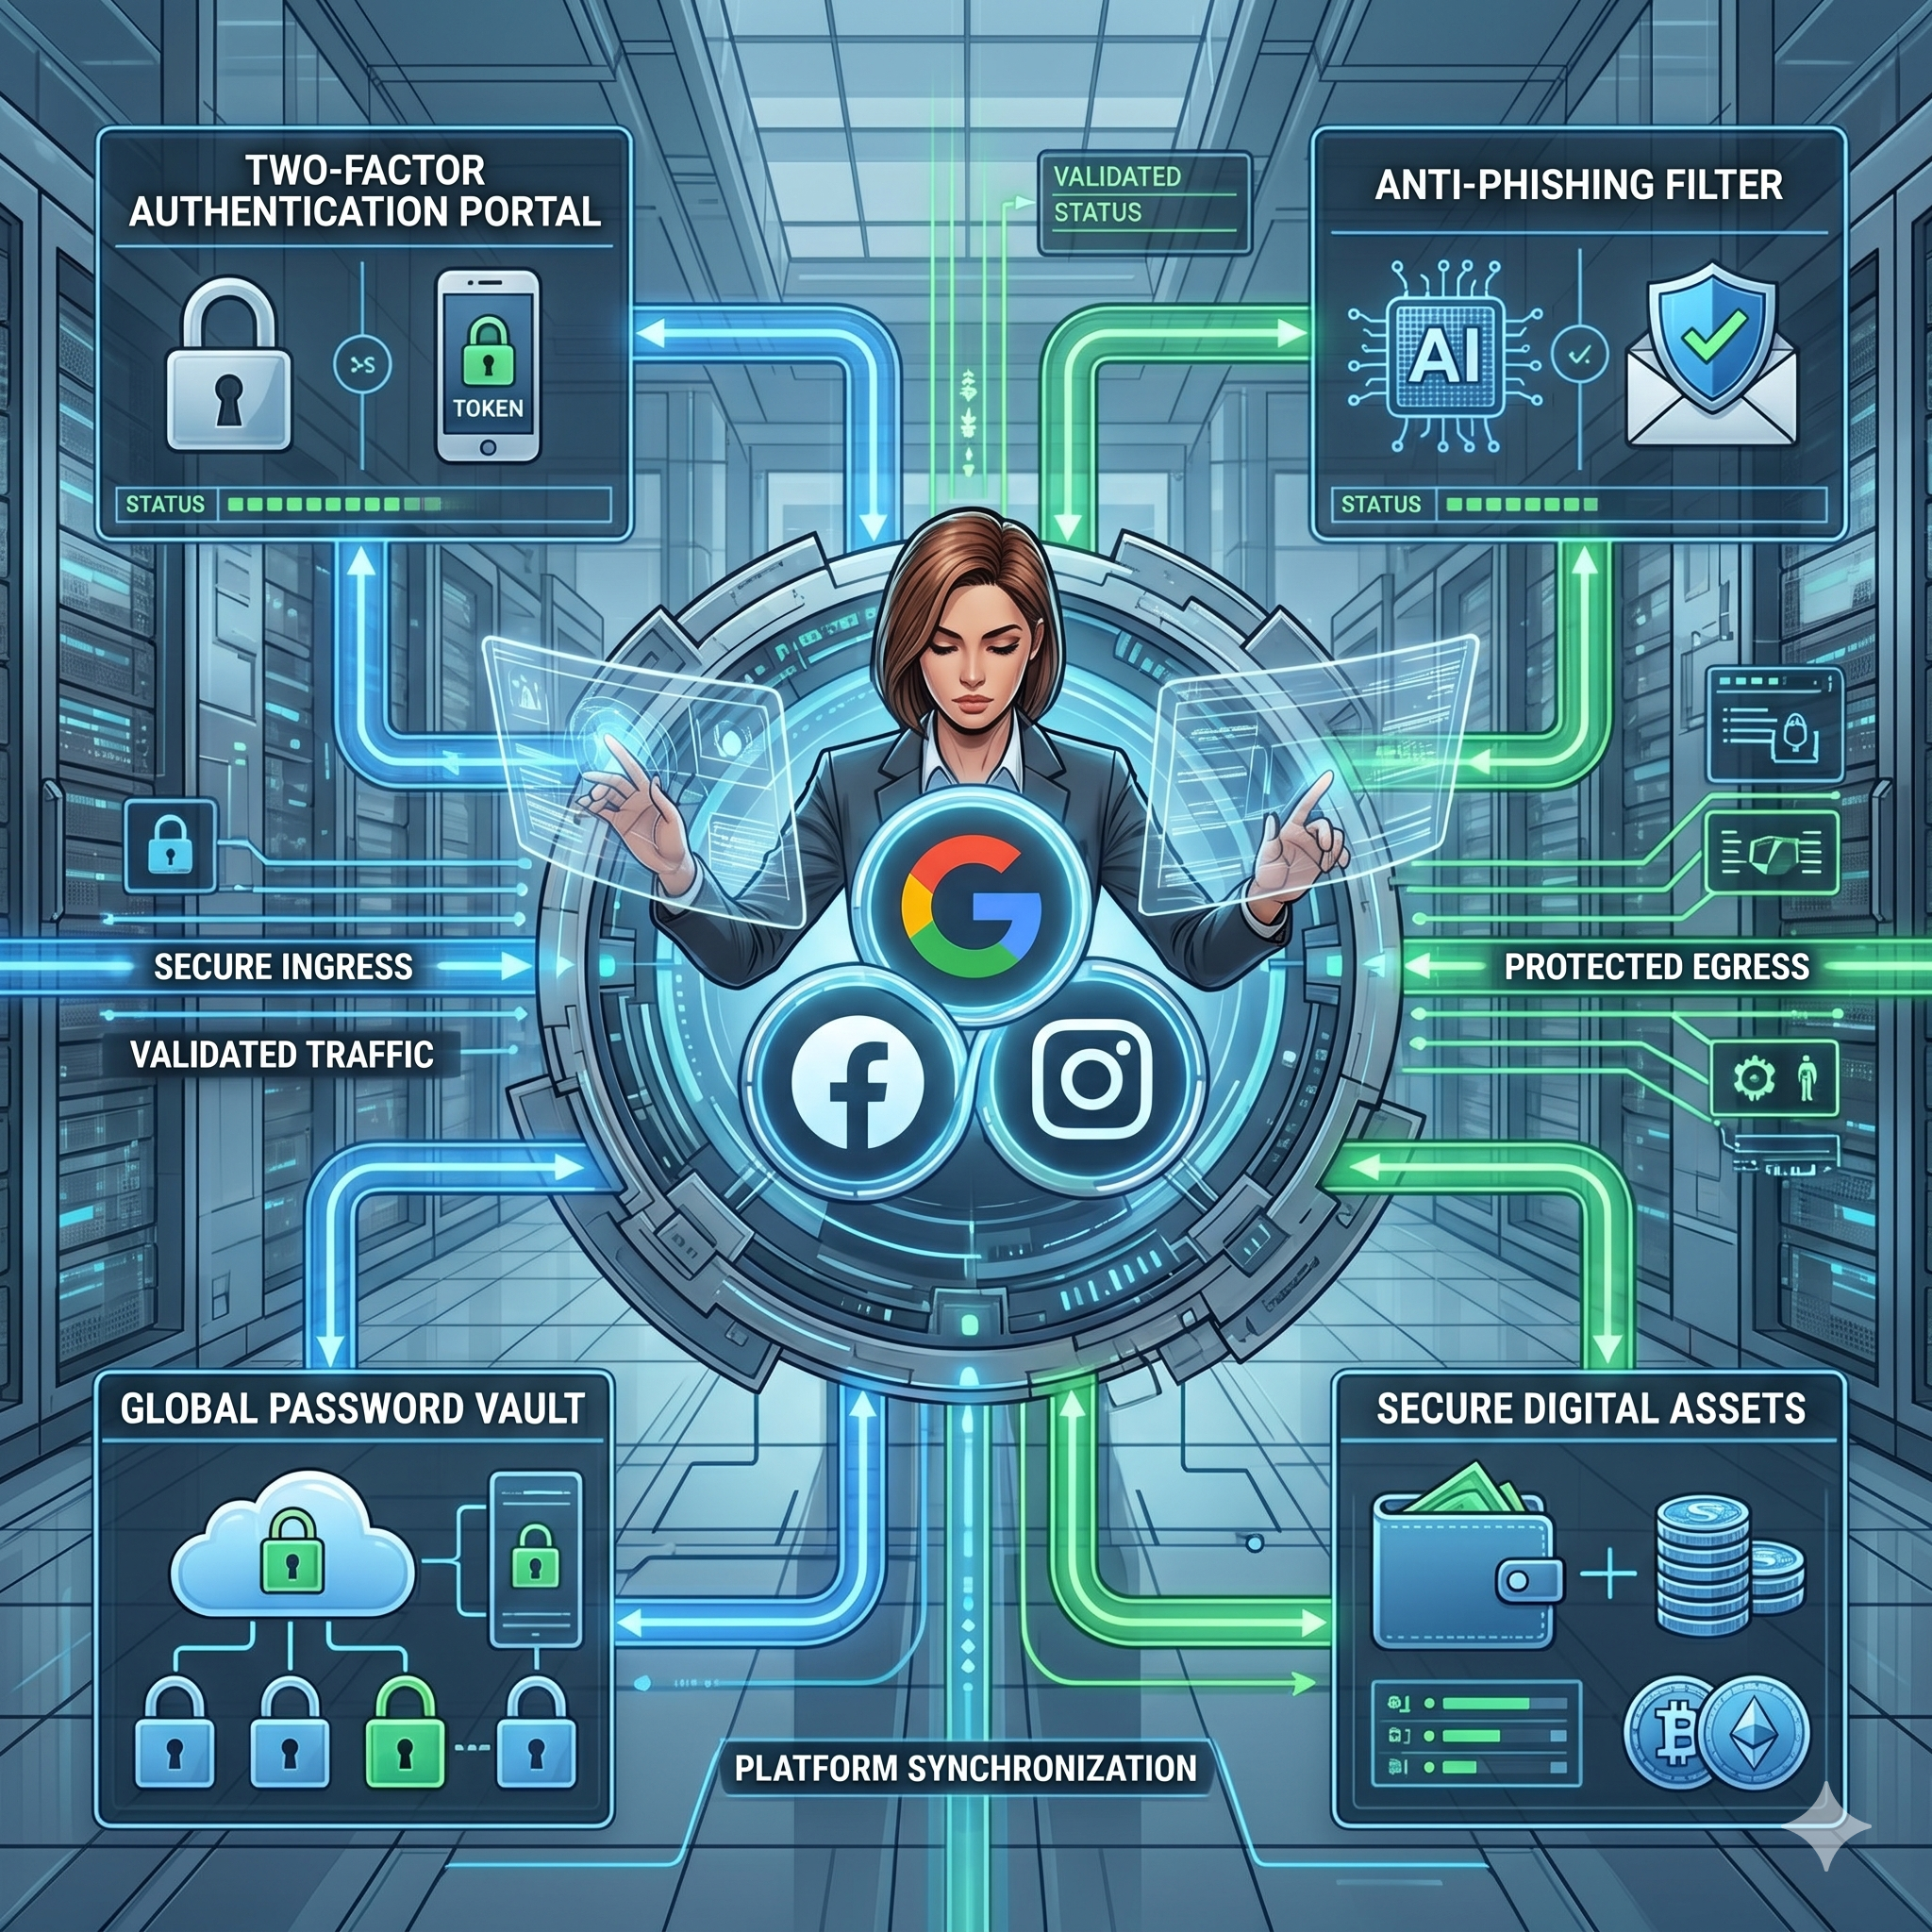
Real defense against account hacks is not a single tool — it is three parallel layers working together: strong authentication, ongoing monitoring, and a pre-planned response for the moment an attack is detected. In 2026, with AI-powered attacks rising sharply, a layered approach is what makes your accounts an unattractive, low-reward target for attackers. Here is how to build it.
The 2026 Threat Landscape
AI now lets attackers craft highly personalized phishing, automate credential-stuffing at scale, and probe for weaknesses in seconds. The realistic question is no longer “will I be targeted?” but “when?” — which is exactly why prevention beats cleanup.
Layer 1: Authentication — Your First Line of Defense
| 2FA method | Security level | Weakness |
|---|---|---|
| SMS code | Basic | Vulnerable to SIM-swap and SS7 attacks |
| Authenticator app (TOTP) | High | Needs physical access to the device |
| Hardware key (YubiKey) | Maximum | Requires physical possession of the key |
| Passkey (biometric) | Very high | Requires device support |
Move critical accounts off SMS toward an authenticator app or, best of all, a hardware key or passkey.
Layer 2: Phishing Detection
Modern AI phishing is nearly indistinguishable from real messages. Watch for:
- Urgency — “your account will be blocked in 24 hours.” Real companies do not manufacture deadlines.
- Suspicious URLs — hover first; g00gle.com ≠ google.com.
- Unexpected code requests — a code you did not request means an attack in progress.
- Wrong sender — check the full email address, not just the display name.
Layer 3: Password Management
A unique, strong password per account is the minimum standard. A password manager (1Password, Bitwarden, Dashlane) generates 20+ character passwords, stores them in an encrypted vault, auto-fills safely, and alerts you when a password appears in a breach — breaking the credential-reuse chain that most hacks rely on.
Business Asset Protection
Teams managing multiple accounts need an extra layer: role-based access (least privilege), monthly session audits of who can reach which accounts, a written incident-response plan for the first hour of an attack, and increasingly, cyber insurance.
When You Need an Expert — How AccRevert Helps
Prevention beats recovery, but when an attack lands, an expert makes the difference — identifying the attack vector, stopping the damage, recovering compromised accounts, and building stronger defenses. AccRevert does exactly that, at a flat $299 to start, success-based after. See our recovery services.
Build Your Personal Incident-Response Plan
The people who recover fastest are the ones who decided what to do before an attack. Write a simple one-page plan and store it somewhere reachable without your main devices: the order to secure accounts (email first, then finance, then social), where your 2FA backup codes and Recovery Key live, the phone numbers for your bank and mobile carrier, and who to notify. Add trusted/recovery contacts on Facebook and Apple ID now, and keep a spare device or eSIM as a backup line. When an attack hits, following a pre-written checklist calmly beats improvising in a panic — and it is often the difference between a quick recovery and a permanent loss.
Frequently Asked Questions
What is the best 2FA method to prevent hacks?
A hardware security key or passkey is strongest, followed by an authenticator app. Avoid SMS for critical accounts — it is vulnerable to SIM-swap and interception.
Can I fully prevent my accounts from being hacked?
No single measure is absolute, but layering strong 2FA, unique passwords in a manager, phishing awareness, and session monitoring makes you a hard enough target that most attackers move on.
How do I protect a business with many accounts?
Use least-privilege role-based access, audit sessions monthly, require 2FA for everyone, keep a written incident-response plan, and consider cyber insurance.
What is the single highest-impact step I can take today?
Put every account’s unique password in a password manager and turn on authenticator-app or hardware-key 2FA. Those two changes defeat the most common attacks.
Final Checklist
- Move critical accounts to authenticator-app or hardware-key 2FA.
- Use a password manager with unique passwords and breach alerts.
- Train yourself and your team to spot phishing and never share codes.
- Audit sessions monthly and keep an incident-response plan ready.
Want to be sure your accounts are properly protected? Talk to AccRevert — don’t wait for the attack to happen.
Related Articles
Stop guessing and document the case properly.
Our team can review the account history, available ownership evidence and the recovery steps already attempted.
Session Cookie Theft: How Hackers Bypass 2FA
Best Password Managers for Account Security in 2026